Hackers Are Using AI to Break Into the Computers That Run Our Water and Power Systems
On August 20, 2026, three U.S. government agencies warned that hackers are targeting a widely used type of industrial computer made by Siemens. These computers, called programmable logic controllers, or PLCs, run machinery in water treatment plants, power stations, factories, and farms. The agencies said attackers are using AI to write attack scripts that find and take over PLCs running outdated software or weak security settings. TechCrunch
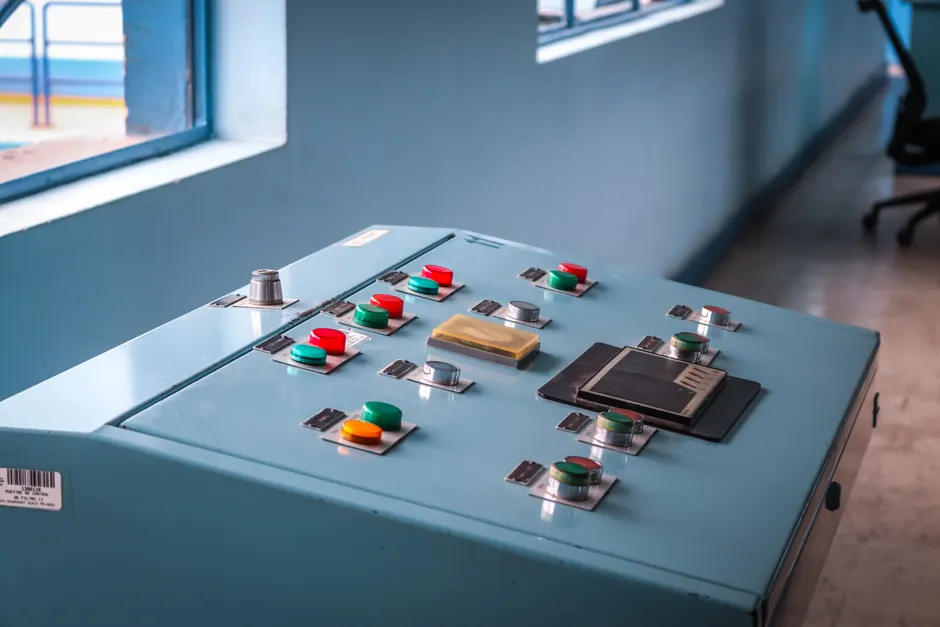
PLCs are the behind-the-scenes computers that open and close valves, regulate water pressure, and control machinery on factory floors. Most people never see them, but they keep essential services running. The Siemens S7 series is one of the most common brands of these devices in the world.
The advisory states that AI dramatically reduces the technical expertise and time required to build these attacks. In the past, someone would have needed deep, specialized knowledge of industrial systems to write working attack code. Now, AI can help bridge that gap. Hackers are also creating scripts disguised as legitimate software to target energy and water systems. Reuters Cybersecurity Dive
CISA said the attacks are part of broader activity targeting water supply and wastewater systems across the United States. Disruption could cause downtime, safety incidents, or equipment damage. Officials have reported break-ins at water facilities in Minnesota, Michigan, Arkansas, Georgia, and New Jersey. The advisory follows a series of cyberattacks by suspected Iranian hackers targeting U.S. water suppliers and wastewater providers in recent months. TechCrunch
The August 20 advisory builds on earlier government warnings. On July 22, CISA, the FBI, the EPA, and other partners issued a joint update warning about Iran-affiliated threat actors targeting water and wastewater systems. The FBI followed with its own advisory on July 30, titled "Malicious Cyber Actors Targeting Water and Wastewater Sector Internet-Facing Programmable Logic Controllers, Causing Operational Disruptions." CISA had also warned in July that hackers were targeting Siemens and Schneider industrial systems. CISA FBI
CISA has long warned infrastructure owners to keep PLCs and similar devices disconnected from the internet. Officials acknowledged that rural communities are often most affected because these systems service large geographic areas, meaning a single compromised facility can disrupt service across a wide region. The current advisory, categorized under Water and Wastewater Systems and titled "Active Threat to Siemens S7 Series PLCs," provides mitigation guidance. CISA Advisory
This advisory also follows a separate December 2025 CISA alert, advisory AA25-343A, which advised operational technology owners on mitigating cyber threats from pro-Russia hacktivist activity. The convergence of state-affiliated and hacktivist threat actors targeting the same class of industrial hardware, now augmented by AI-generated tooling, compounds the risk for operators who have already been warned about internet-facing PLCs. CISA
The AI dimension is the genuinely new factor here. The industrial control system community has long assumed that effective attacks on these systems require deep, specialized knowledge of specific vendor hardware and protocols. That assumption still partly holds, but the advisory indicates that AI is shortening the time and reducing the expertise needed to turn publicly available information about a PLC into a working attack script. For a sector where software updates are measured in months and sometimes quarters, the threat timeline has gotten shorter.
The geographic spread of reported intrusions, from Minnesota to Georgia to New Jersey, reinforces what CISA and the FBI have been stressing since at least July: the water and wastewater sector's spread-out, under-resourced character makes it a broad target. Rural systems, which may lack dedicated cybersecurity staff, face greater risk. The advisory's guidance focuses on reducing internet exposure of S7-series PLCs, patching outdated software, and separating industrial control networks from ordinary business computer networks so an intruder in one cannot freely reach the other.
For operators, the actionable guidance is narrow and familiar: disconnect these devices from the internet where possible, separate networks where you cannot, and treat every internet-connected PLC as a likely target. The novelty is not in the defensive advice but in the offensive acceleration that now makes that advice urgent.