Hackers Hit Over 100 U.S. Water Systems — Here's What Happened

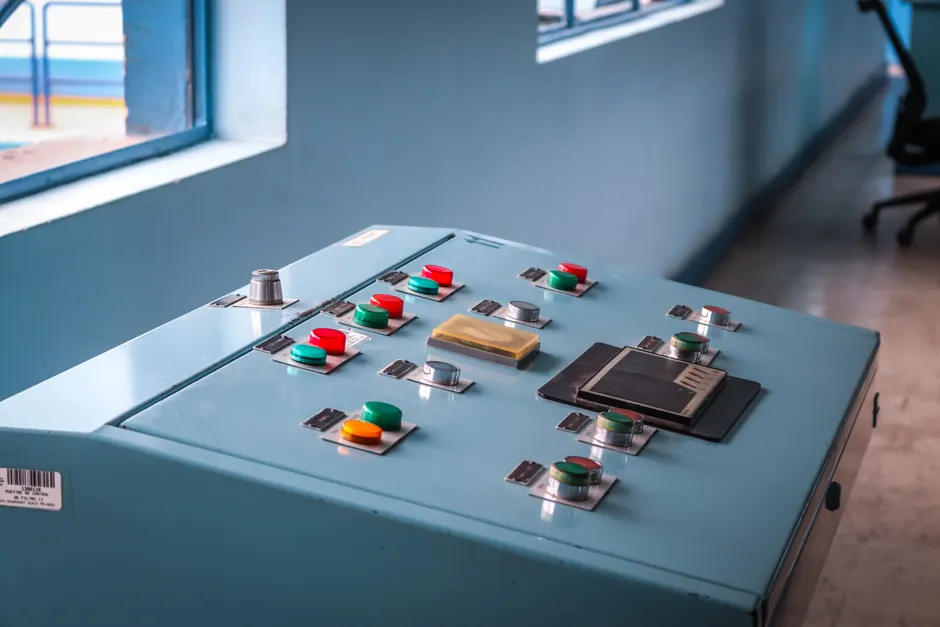
CISA, the federal agency responsible for cybersecurity, has confirmed that hackers attacked more than 100 water and wastewater systems across the United States during July 2026. The attacks mostly targeted devices called programmable logic controllers, or PLCs. These are the industrial computers that control physical machinery at water utilities, energy systems, and other critical infrastructure. (TechCrunch, 2026-08-26)
The affected PLCs were made by Rockwell, Schneider Electric, and Siemens. CISA had previously reported that the hackers were able to change settings on these devices in ways that turned off safety shutdown processes and alarms. That means unsafe conditions could have developed without the people running the systems even knowing. In at least some cases, the hackers used AI tools that gather publicly available information to write code targeting vulnerable Siemens PLCs. (TechCrunch, 2026-08-26)
The attacks did not actually affect the water or wastewater that reached communities. They did cause outages and disruption, though, as teams investigated the breaches and worked to secure the systems. Many of the communities hit are in rural or isolated areas, where water utilities typically have smaller staffs and smaller cybersecurity budgets than those in cities. (TechCrunch, 2026-08-26)
Affected providers span Michigan, Minnesota, and at least five other states. The FBI issued an alert on July 30, 2026, stating that since July 27, 2026, water and wastewater utility companies in at least seven states had reported incidents. (FBI, 2026-07-30)
CISA's response grew across the summer. On July 22, 2026, the agency published a cybersecurity advisory stating that hackers linked to Iran had exploited PLCs and compromised at least 75 devices, including some used across multiple critical sectors. That same day, CISA, the FBI, the EPA, and other U.S. government partners updated a joint warning that Iranian-affiliated threat actors are targeting internet-connected operational technology — the computers and devices that control physical infrastructure. The advisory noted that the actors used several foreign-based IP addresses to access internet-facing systems. (CISA, 2026-07-22) (CISA, 2026-07-22)
Following the attacks in Minnesota, CISA urged water utilities to take exposed systems offline entirely. Nextgov reported that some U.S. officials believe an Iran-aligned cyber group is behind the campaign, citing two people familiar with the matter. (Nextgov, 2026-07-31)
Senior American officials say U.S. intelligence assesses that Iran is likely behind the attacks, probably in response to the U.S. and Israel-led war against Iran, though officials have not provided definitive proof. The campaign appears opportunistic, meaning the hackers were not targeting specific high-value sites. Instead, they seem to have scanned the internet for exposed PLCs and attacked whichever ones they could reach. (TechCrunch, 2026-08-26)
This is not the first time hackers linked to Iran have been connected to PLC attacks in the U.S. water sector. A CISA advisory updated as recently as December 2024 documented Iranian cyber actors exploiting PLCs across multiple sectors including U.S. water and wastewater facilities. And in 2026, CISA released an updated advisory titled "Iranian-Affiliated Cyber Actors," highlighting continued targeting that includes the water and wastewater sector. (CISA, 2024-12-18) (CISA)
The pattern is familiar to anyone who has followed security for industrial systems over the past decade. PLCs connected to the internet with default or weak passwords have been a known problem since at least the mid-2010s, when researchers began routinely showing they could remotely access these controllers using Shodan, a search engine that finds internet-connected devices. What has changed is that AI tools now make it easier for hackers to write working attack code for specific PLCs, and the geopolitical situation gives a state-linked actor reason to cast a wide net rather than carefully select high-value targets.
The operational impact here matters less than the trajectory. No community lost water service. But the ability to turn off safety shutdown processes and alarms on industrial controllers, even by scanning randomly, means the attackers reached a level of access where physical consequences were possible, not just theoretical. For rural utilities that may not have a dedicated security expert on staff, the gap between a successful hack and a real safety incident is narrow, and depends heavily on whether there are mechanical backup systems in place beyond the digital controls.
CISA's recommendation that utilities take exposed systems offline is straightforward advice, but it surfaces a structural problem. Many of these PLCs were designed to be accessed remotely for legitimate reasons, often by outside contractors or vendors providing maintenance support. Taking them offline removes the risk, but it also removes the remote access that smaller utilities may rely on. The longer-term fix involves separating these control networks from the internet and adding proper passwords and authentication to PLC interfaces, but that requires money and expertise that rural water districts do not all have.
The federal coordination across CISA, FBI, and EPA reflects an understanding that the water sector's fragmentation — tens of thousands of mostly small utilities operating independently — makes it vulnerable to exactly this kind of broad, opportunistic scanning campaign. Whether that coordination leads to lasting funding for security improvements at the local level is a separate question, and one that previous federal water-sector cybersecurity initiatives have not fully answered.
In my view, the most important takeaway is that AI-assisted exploit development has moved from a research demonstration to a factor in active, state-linked campaigns against U.S. infrastructure. That is a meaningful threshold, even if the immediate damage in this case was contained.