Flock Has Never Fired a Police Customer, CEO Says

Flock has not ended any customer contract over misuse of its products, CEO Garrett Langley said on Oct. 14, 2026, during an on-stage interview at Disrupt 2026 in San Francisco. TechCrunch
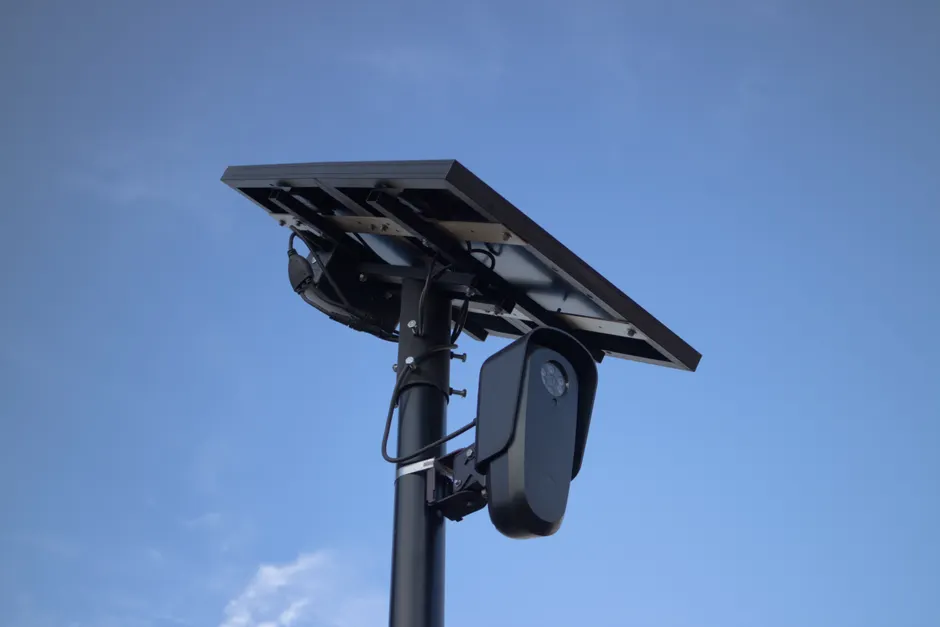
Speaking with TechCrunch editor-in-chief Connie Loizos, Langley said the Atlanta, Georgia-based maker of license plate reader cameras — cameras that record plate numbers with time and location — has not to date “fired” any customer such as a police department or law enforcement agency. He was unequivocal on that point. The company operates more than 100,000 cameras around the United States.
Langley set a threshold for future action. He said Flock would end a customer relationship where there was clear widespread abuse of its systems. “If a customer knowingly broke the law, we would fire them immediately.”
He also said Flock does not have a direct contract with U.S. Immigration and Customs Enforcement. Langley is co-founder of Flock Safety. Flock Safety
Demonstrators protesting Flock’s surveillance gathered outside the Disrupt venue while Langley spoke on stage.
The interview followed workforce reductions at the company. Flock is reducing its staff by 18%, or around 270 employees. TechCrunch Flock had reportedly tried to shrink its workforce through employee buyouts about three weeks earlier. TechCrunch
On controls, Flock Safety said in August that more than one-third of its customers had voluntarily adopted Audit Assistance, a logging tool that records who searched the system and why, and that it will require all law enforcement customers to adopt it. Flock Safety In earlier company statements, Flock Safety stated its private customers never have access to law enforcement data, and stated it does not presently have a contractual relationship with any U.S. Department of Homeland Security agencies.
The broader context here is the gap between a written policy and an enforcement record. A vendor can publish use rules, provide auditing tools, and require adoption across its installed base without ever having ended a contract. That does not make the policy empty. It does mean customers, oversight boards, and the public have only the vendor’s description of where the line sits, not a case history showing how it applies that line in practice.
In my view, technology professionals should read this mainly as a governance question about data access, not only as a debate about surveillance. The readers work as distributed sensors feeding a central search interface. The hard questions are familiar to anyone who runs shared systems. Who can query what, under what authorization, with what logging, and with what review. Voluntary adoption followed by a mandate is a standard enterprise pattern. The test is whether those audit trails are complete, hard to alter, and checked by someone other than the operator being audited.
Looking at what this means for buyers and operators, the stated intent to terminate for knowing illegality or clear widespread abuse puts the focus on detection. A security chief would ask how widespread is defined when federated agencies share data, how knowing conduct is established, and how quickly access can be suspended pending review. Those are operational details, not slogans. If Flock and its law enforcement customers can answer them plainly, the technology becomes easier to evaluate on outcomes like clearance rates and exonerations, which is where durable trust tends to come from.